Protecting Yourself While Travelling: Public Wi-Fi and Hotel Network Risks
08/10/2026
By: Fidelity Bank

Customer Security Advisory
Protecting Yourself While Travelling: Public Wi-Fi and Hotel Network Risks
Issued: 5 August 2026
Audience: All Fidelity Bank customers, with particular relevance to frequent travelers and business customers.
Why we are sending this
Security researchers have identified an active campaign in which criminals compromise public Wi-Fi and "captive portal" login pages at hotels, airports, cafes, conference venues, and other shared networks worldwide.
Security researchers report that attackers are now using AI to build and adapt this malware, making the attacks faster, harder to detect, and more convincing than earlier versions of this scam.
This advisory explains the risk in plain terms and gives practical steps to protect your accounts, including your Fidelity Bank online and mobile banking access.
What Is Happening
When you connect to public Wi-Fi — at a hotel, airport, cafe, gym, library, or anywhere else — your device is normally shown a “captive portal” login page. Criminals have found ways to compromise this process at some venues, showing a fake software update, network tool, or sign-in prompt instead. Following the on-screen instructions installs malware that can steal passwords, banking sessions, files, and keystrokes, and give attackers ongoing remote access to the device.
What makes this wave more dangerous: researchers say AI has been used to help write and refine the malware and phishing pages, making them faster to deploy, better at evading security software, and more convincing to the people they target.
Who Should Pay Attention
- Anyone who connects a laptop, tablet, or phone to any public or guest Wi-Fi, whether travelling or simply out and about.
- Customers who access Fidelity Bank online or mobile banking, email, or cloud storage on any network outside their home or office.
- Business customers and staff attending conferences, and Android phone users, who have been specifically targeted.
Warning Signs to Watch For
- A Wi-Fi login page that asks you to download or run a program, or an “update” or “diagnostic” tool, before you can get online.
- Any prompt to open a command window and paste in a command — a legitimate Wi-Fi login page will never ask this.
- A pop-up asking you to enter a “device code” into a separate Microsoft sign-in screen to “register” your device.
- A Wi-Fi page that looks slightly off, has spelling errors, or urgently pressures you to act.
How to Protect Yourself
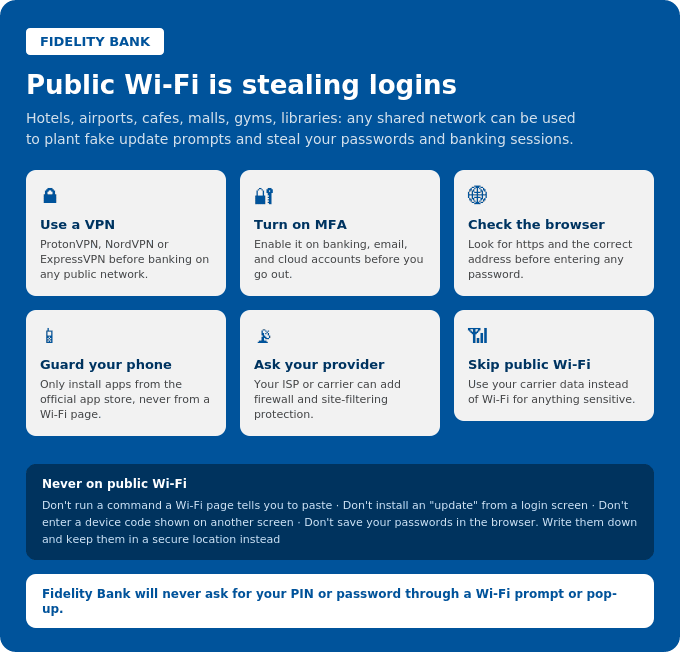
- Never run a command or install software prompted by a Wi-Fi login page. Only install updates through your device’s official settings or app store.
- Be cautious with device-code sign-in prompts — stop and verify independently before entering one.
- Use a trusted VPN (ProtonVPN, NordVPN, ExpressVPN, or your employer’s corporate VPN) before banking or working on any public Wi-Fi.
- Where possible, use your mobile carrier’s data or a personal hotspot instead of public Wi-Fi for anything sensitive.
- Keep your device, browser, and apps updated, and confirm MFA is switched on for banking, email, and cloud accounts before you travel.
- Never approve an MFA or sign-in prompt you did not personally initiate; decline it and contact us immediately.
Quick Check Before You Travel
- Confirm MFA is enabled on your Fidelity Bank, email, and cloud accounts.
- Install a reputable VPN app from the official app store or provider website.
- Update your device and apps while on trusted home or office Wi-Fi.
Browser and Device Protections
Much of this campaign works by getting you to type a password, or approve a sign-in, inside your browser or on your phone. A few habits close off most of this risk:
- Keep your browser updated, and check for the padlock icon and correct web address before entering any password.
- Use a password manager instead of typing passwords from memory — it will not auto-fill credentials into a fake look-alike site.
- Avoid saving your Fidelity Bank password in the browser on a shared or public computer, and clear cookies/sessions after banking on public Wi-Fi.
- Only install apps from the official app store, never from a Wi-Fi page, and keep “install unknown apps” switched off on Android.
- Use your phone’s screen lock, biometric login, and “Find My Device” in case it is lost or stolen.
Ask Your Internet and Mobile Provider About Network Protection
Your home internet provider and mobile carrier can often add protection before a threat reaches your device. Consider asking about router/firewall settings, DNS or phishing-site filtering, and mobile threat protection add-ons. Business customers should ask their IT provider about enterprise firewalls and secure web gateways for staff who travel.
If You Think You May Have Been Affected
- Disconnect the device from Wi-Fi and avoid using it until checked by a trusted IT professional.
- Change your passwords immediately from a different, trusted device — starting with banking and email.
- Contact Fidelity Bank promptly to review recent account activity.
- Review your statements and transaction alerts closely over the following weeks.
Fidelity Bank Will Never
- Ask you to enter your online banking password, one-time PIN, or card details in response to a Wi-Fi prompt, pop-up, or unsolicited message.
- Ask you to run a command, script, or troubleshooting tool on your device to “verify” your account.
- Ask you to approve a sign-in or device-code request that you did not initiate yourself.
Need Help or Have a Concern?
If you notice suspicious activity on your account, receive an unexpected authentication request, or simply want to verify whether a message or prompt is genuine, please contact Fidelity Bank directly through the official customer service number on the back of your card or on our verified website. Do not use contact details provided within a suspicious pop-up, email, or Wi-Fi page.
This advisory is provided for general customer awareness based on published third-party security research. It does not constitute technical or legal advice. © Fidelity Bank — Customer Security Advisory